




The solution: autonomous exposure validation
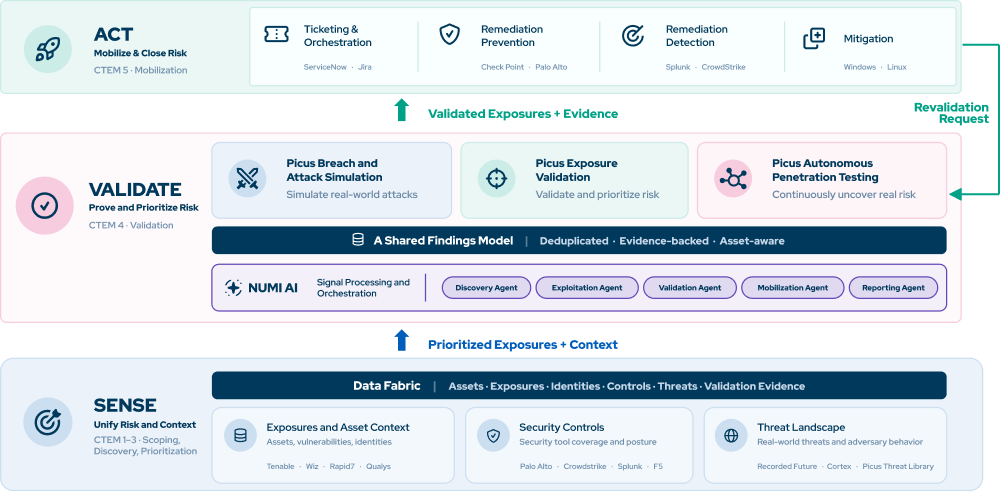
Three Products. One Platform. No Blind Spots Left.
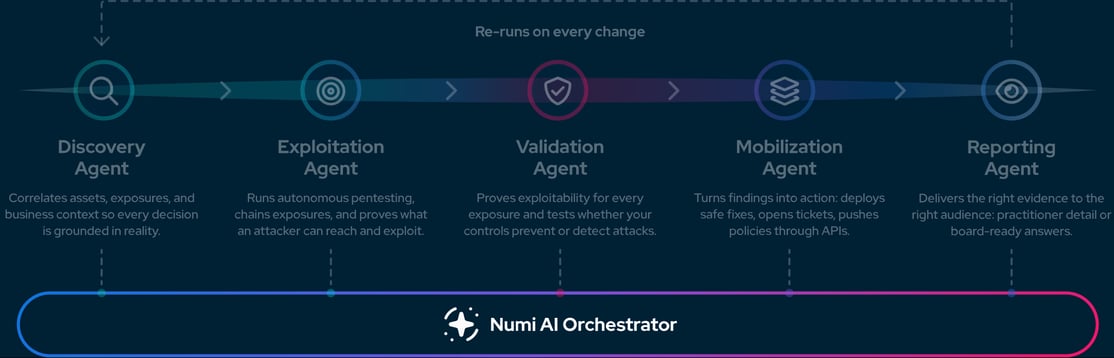
Controls stop what patches never will. Agents run on signal, not schedule.
Every finding, from any source, gets a defensible decision and closes with evidence.
The innovation
Picus Swarm™
The only team of specialized AI agents that converges automated pentesting, exposure validation, and breach and attack simulation into one autonomous, context-aware loop; with autonomy you tune, from manual to fully autonomous.
Proof
300M+ attack simulations. Last year alone.
Run safely in live production across more than 600 enterprises. Customers’ Choice on Gartner Peer Insights, number one in Breach and Attack Simulation on G2, Innovation Leader on the Frost Radar.
-
~9 min
intel to runnable simulation
-
Day one
exploitability verdict, no exploit
-
2x
control effectiveness in 90 days
-
89%
faster remediation
-
92%
fewer SLA violations
-
86%
backlog reduction
-
4.8 / 5 · 98% recommend
“A game-changer in security validation. Intuitive platform, clear reporting, and actionable insights that measurably improved our posture.”
Cyber Security Team Lead · Mid Market
Proof
Trusted by Security Teams, Recognized by the Industry
-
Customer's Choice
Gartner Peer Insights Voice of the Customer Adversarial Exposure Validation
-
BAS Category Leader
#1 Breach and Attack Simulation
(BAS) Solution
-
#1 Leader Frost Radar
The Innovation Leader in
Automated Security Validation
Why Picus
Point Tools Answer a Fragment.
Picus Delivers All.
Siloed validation tools are strong on their slice and silent elsewhere. Exposure assessment platforms aggregate well, but configuration analysis is not validation. Only one loop turns every row green.
| Validation Criteria | Siloed Validation ToolsPentest, bug bounty, simulation, each on its own | Exposure Assessment PlatformsScan, aggregate, score | Picus PlatformOne loop, three techniques |
|---|---|---|---|
| Evidence of real exploitability | Each on its own slice | Configuration analysis, not validation |  All three techniques, proof attached |
| Covers restricted and air-gapped assets | No | No | No live exploit required |
| One pipeline for every source | No | Own findings only | Pentest, bug bounty, red team, simulation, scanner |
| Verdict on the day of disclosure | Not until an exploit exists | No | Day one, per asset |
| Signal-driven, not scheduled | No | No | Fires once per relevant change |
| Machine-speed execution, governed | No | No | Tunable autonomy, humans set the rules |
| Organization-specific scoring | Limited | Generic severity | Picus Exposure Score and Asset
Score |
| Proven closure through re-validation | Manual re-run | Closed when the ticket closes | Automated re-validation on every change |
Resources
Discover Our Latest News and Content
-
Node2Shell (CVE-2026-111497): Node.js Brotli RCE Vulnerability Explained
-
Famous Chollima APT Group: Major Activities, TTPs, and Simulation
-
What PHP2Shell Reveals About the Limits of Automated Pentesting
-
PHP2Shell: Critical PHP RCE Flaws (CVE-2026-109618 & CVE-2026-109619) Explained
-
CVE-2026-88771: Citrix NetScaler Pre-Auth Command Injection Explained
-
CISA AA26-281A: How Chinese Government-Linked Actors Steal Sensitive Data
-
CVE-2026-94127 Explained: F5 BIG-IP APM Heap Overflow Attack
-
How Click2Shell Exploits WordPress Theme Installation for RCE
-
FSB Center 16: How Russian hackers exploit routers via SNMP and Cisco Smart Install