Prove what attackers can actually exploit

Autonomous Penetration Testing

Picus runs autonomous agents that chain real attacks across your full environment to show which exposures are genuinely exploitable.

  • Safely hack your environment. AI agents run real attacks against your production environment, with guardrails you control.
  • Act on real risk. Prioritize exposures by validated risk and blast radius, remediate the ones that matter most, then verify the fix.
  • Decide on evidence. Patch, Mitigate, Monitor, or Accept Risk, each call backed by a validated exploit chain, not a static score.
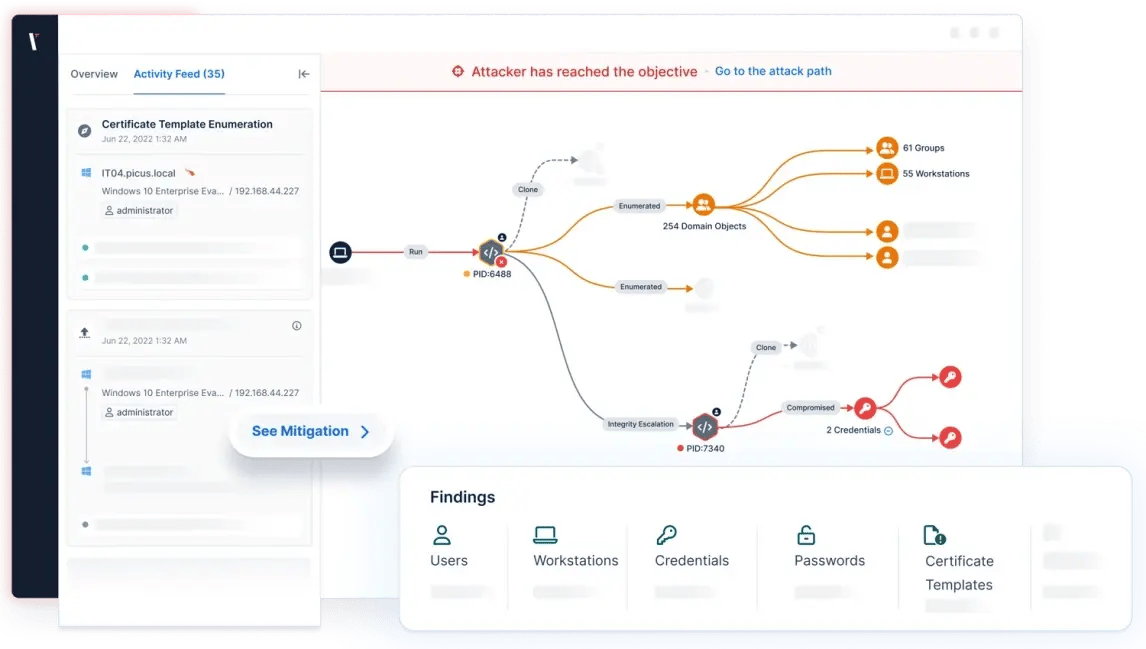
Picus Autonomous Penetration Testing: an attack path that reaches the objective, with findings for users, workstations, credentials, passwords and certificate templates

Why Now

Finding the exposure was never the hard part. Proving the right call is.

AI has collapsed the time between disclosure and attack. New vulnerabilities are weaponized in hours, and adversaries break out in minutes. Teams are not short on findings. They are short on defensible answers.

  • Backlog grows faster than anyone can clear it

    Known exposure accumulates faster than any team can safely remediate. With roughly 135 new CVEs a day and a 0.5% ever patched, the risk window stays open.

  • Knowing a CVE exists is not knowing it works here

    Teams can see which vulnerabilities exist, but not whether the exploit would actually succeed against your controls, in your environment.

  • Every call rests on scores and assumptions

    Patch, mitigate, monitor, or accept. When attacks happen in minutes, teams cannot prove which decision is defensible to auditors or the board.

The answer is not another scanner list, more visibility, or more headcount. It is autonomous exposure validation that knows your environment and proves what an attacker could actually do in it.

How it works

AI agents find, exploit, and prove what matters.

The answer is not another scanner list, it is Picus Autonomous Penetration Testing that knows your environment and proves what an attacker could actually do in it. Agents reason and chain techniques like a real attacker, continuously.

  1. Recon

    Map the attack surface

    Continuously enumerate external assets, internal networks, identities, and misconfigurations across the environment.

  2. Exploit

    Chain real exposures, safely

    Autonomously execute real-world exploitation techniques and chain exposures across hosts, within the guardrails you set.

  3. Prove

    Demonstrate true impact

    Reach crown-jewel assets and capture concrete proof of compromise. This is proof, ordered by blast radius, not another ranked list.

  4. Prioritize

    Fix what actually breaks you

    Rank remediations by real exploitability and blast radius, then re-validate the specific path you fixed. Loop until clean.

Then it loops, continuously, re-validating as your environment changes.

Benefits

Outcomes You Can Act On

  • Focus on exploitable exposures

    Prove which exposures attackers can actually reach and weaponize, so you can act on real risk.

  • Operate at machine speed

    Weeks of manual pentesting compressed into minutes. Continuous and on demand, so the picture is always current, never a snapshot.

  • Reveal critical attack paths

    Chained weaknesses cause breaches. Map the full chain from foothold to crown jewels and show exactly where to break it.

  • Get attacker-grade findings your team can act on

    Agents handle the offensive execution and reasoning, so your team receives validated findings and prioritized paths.

  • Close the loop with one-click re-validation

    Test fixes the moment they ship. Picus re-runs the exact path you remediated to confirm the gap is closed in minutes.

  • Autonomy without losing control

    Run fully autonomous, fully supervised, or anywhere in between. Every action and decision is logged end to end.

The coverage question

A standalone pentest tool can only validate a fraction of your security program.

Across organizations, 95% rank pentesting a top priority, yet just 32% of the global attack surface gets tested on average. That leaves roughly two-thirds of the environment untested.

  • ~68%

    of the attack surface of an enterprise goes untested, beyond the reach of pentesting.

    Synack & Omdia, 2026

  • 1 in 3

    known ransomware CVEs from 2025 still had no public or commercial exploit to fire as of January 2026.

    VulnCheck Exploit Intelligence Report, 2026

  • ~0.6%

    of CVEs is weaponized, highlighting the limits of relying on exploitation alone to understand the exposure.

    VulnCheck Exploit Intelligence Report, 2026

The Picus Platform

One Platform Validates Your Whole Security Program.

Autonomous Penetration Testing is one part of the Picus Platform. Together, these capabilities converge into one continuous validation loop, from attack surface to controls to exploitable exposures.

Proof

Trusted by Security Teams, Recognized by the Industry

  • Outstanding Experience with Picus – A Game-Changer in Security Validation. The platform is intuitive, the reporting is clear, and the actionable insights significantly enhance our overall security posture.

  • It allows me to test current cyber attack scenarios within my own environment, which is extremely valuable for improving our security posture.

Resources

Latest Resources on Automated Penetration Testing

  • How Much Does Automated Penetration Testing Cost?

    How Much Does Automated Penetration Testing Cost?

  • Automated Pentesting vs Automated Red Teaming: What’s the Difference?

    Automated Pentesting vs Automated Red Teaming: What’s the Difference?

  • Where Does Automated Pentesting Fit in CTEM?

    Where Does Automated Pentesting Fit in CTEM?

FAQ

Frequently Asked Questions

About Autonomous Penetration Testing

What is Picus Autonomous Penetration Testing?

It uses autonomous AI agents to discover vulnerabilities, develop and chain exploits, and execute real attack campaigns against your environment. Rather than running as a periodic test, it operates continuously, reasoning and adapting like a real attacker to prove which exposures are genuinely exploitable.

How Is This Different From Manual Penetration Testing?

Manual pentesting delivers human-led depth within a limited scope, typically once or twice a year. This automates the work that does not need continuous human involvement, exploit chaining, attack-path validation, and post-remediation re-testing across the full surface, so it stays current as the environment changes. The strongest programs use both: automation for scale and frequency, humans for bespoke adversary emulation and novel research.

Does It Replace Red Teaming?

No. Red teams remain essential for bespoke adversary emulation, novel attack research, business-logic abuse, and complex human-driven operations. This handles the continuous, repeatable offensive work so your red team can focus where human creativity matters most.

Is It Safe To Run in Production?

Yes, when operated with proper guardrails. Tunable autonomy controls let you define scope, restrict techniques, and require human approval where needed. Every action is logged end to end with complete operational traceability and chain of custody.

What about assets a live exploit can never safely touch?

Live exploitation can only validate the fraction of your environment it can safely reach and actively exploit. For business-critical, restricted, and air-gapped assets, CVEs with no working exploit, and the day-one window before an exploit exists, Picus Exposure Validation maps the CVE to its TTP chain and validates it against your controls without firing a live exploit. Together with Picus Breach and Attack Simulation, that is how the loop covers what live testing cannot.

How often should it run?

Continuously. Modern attack windows move too fast for scheduled assessments. Picus operates in a signal-driven model, responding autonomously to new CVEs, infrastructure changes, configuration drift, and emerging threat intelligence as they appear.

How does it work with our existing tools?

It integrates with vulnerability scanners, ASM tools, SIEMs, EDRs, and operational workflows to normalize findings, validate exploitability, prioritize real exposure, and push validated results into your existing remediation and detection pipelines, with evidence attached.

See How Picus Platform Works

  • See Picus Run on Your Environment

    In a live demo, watch Picus validate a real exposure end to end, from exploit to fix to re-test.

  • Discover the Platform

    Simulate real-world cyber threats in minutes and see a holistic view of your security effectiveness.